
DTS Solution Upgrades Penetration Testing, VAPT and Red Teaming Services in Kuwait
DTS Solution brings upgraded penetration testing, VAPT and red teaming services to organizations across Kuwait.
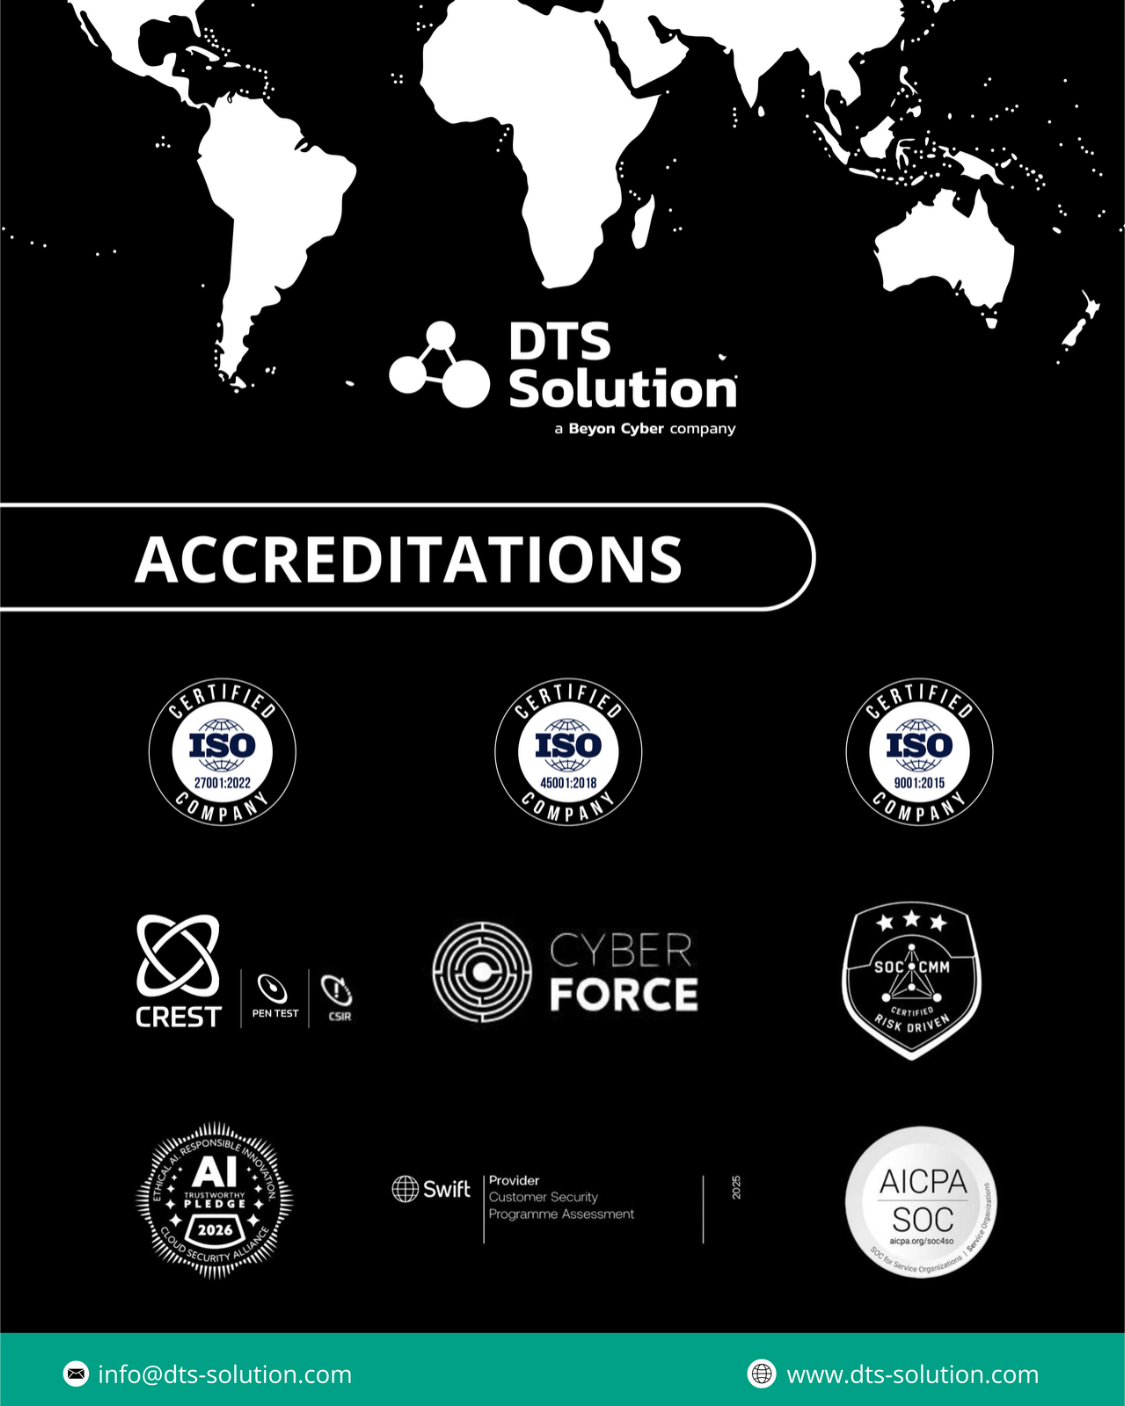
DTS Solution’s accreditations, including CREST, behind its penetration testing, VAPT and red teaming services in Kuwait.
CORF-aligned red teaming, threat-informed vulnerability assessment and penetration testing, and board-ready reporting from DTS Solution's Kuwait City team.
What changes in DTS Solution's penetration testing services
> Threat-informed penetration testing: test scenarios built around each client's sector, critical systems and suppliers, instead of a generic checklist.
> CORF-aligned red teaming: annual red team programmes for CBK-regulated entities, with additional exercises when critical systems, threats or regulations change.
> Two-layer reporting: an executive summary for boards and regulators, alongside technical findings with risk ratings, proof of exploitation and step-by-step remediation.
> Retesting before close: every penetration test and red team engagement ends with a retest that confirms fixes work.
> Purple teaming with HawkEye: clients monitored by HawkEye, DTS Solution's managed detection and response service, can turn penetration testing and red team findings into tuned detection rules.
What is VAPT?
VAPT stands for vulnerability assessment and penetration testing. A vulnerability assessment scans systems, applications and networks to identify and rank known weaknesses, such as missing patches, outdated software and insecure configurations. Penetration testing goes further: certified ethical hackers exploit the weaknesses that matter, manually, to show what a real attacker could reach and how separate flaws chain together into a breach.
The two work best together. A vulnerability scan on its own produces a long list without business context, and a penetration test on its own covers a narrower scope. Combined, VAPT gives organizations in Kuwait both coverage and proof of real-world impact.
Penetration testing services in Kuwait
DTS Solution's penetration testing services run as black box, grey box or white box tests, depending on how much the client wants the testers to know in advance, as listed on its CREST supplier profile.
The upgraded service covers:
Web application penetration testing: testing for the OWASP Top 10, including injection, broken access control and authentication flaws, plus business logic weaknesses that automated scanners miss.
Mobile application penetration testing: iOS and Android testing for insecure data storage, weak cryptography and the APIs behind the app.
Network penetration testing: external testing of internet-facing systems and internal testing that shows how far an attacker could move once inside the network.
API and cloud penetration testing: authentication, authorization and configuration testing for APIs and cloud workloads.
Wireless penetration testing: testing corporate and guest Wi-Fi for weak encryption, rogue access points and network segmentation gaps.
Social engineering testing: phishing and pretexting campaigns that measure how staff respond to manipulation.
Red teaming and adversary simulation
A penetration test shows where an organization is exposed. Red teaming tests whether the organization would notice a real attack and how quickly it would respond. The red team works covertly toward agreed objectives, such as reaching payment systems or customer data, and the defending security operations team is not told when the attack starts.
Each DTS red team engagement measures four outcomes: whether the attack was detected, how long detection took, how long the response took, and whether the response was the right one. Most organizations need both: penetration testing on a regular cycle and after significant changes, and red teaming once the main findings have been fixed.
Penetration testing and compliance in Kuwait
Several frameworks that apply in Kuwait expect regular penetration testing or adversary simulation:
CBK CORF: the Central Bank of Kuwait's Cyber and Operational Resilience Framework, which replaced the 2020 Cybersecurity Framework for banks and financial institutions, requires red teaming at least once a year, or sooner when threats, critical systems or regulations change.
PCI DSS: organizations that store, process or transmit card data must run internal and external penetration tests at least once a year and after significant changes.
SWIFT CSCF: banks connected to SWIFT use penetration testing to show that their secure zone and connected systems are protected.
CITRA and ISO 27001: telecom and digital service providers working toward CITRA compliance, and organizations certified to ISO 27001, use VAPT as evidence of technical vulnerability management.
How a DTS penetration test runs
Scoping and rules of engagement, agreed with senior leadership before testing starts
Threat-informed test design based on the client's sector, systems and suppliers
Vulnerability assessment and manual penetration testing by certified consultants
Reporting in two layers, for the board and regulator and for the technical team
Retesting to confirm fixes before the engagement is signed off
“Our clients in Kuwait have relied on our penetration testing and red team work for years, and the questions they now get from regulators and boards have changed,” said Vahe Daghlian, CEO and Co-Founder of DTS Solution. “These upgrades give them clearer proof of three things: where an attacker can get in, whether their team sees it, and how fast they respond.”
Organizations can book a penetration test, VAPT or red team scoping session by emailing info@dts-solution.com.
About DTS Solution
DTS Solution, a Beyon Cyber company, has served organizations across the GCC since 2011, with offices in Dubai, Abu Dhabi, Kuwait City and Riyadh. Its services span cybersecurity advisory, GRC, penetration testing and offensive security, incident response and 24/7 managed detection and response through HawkEye. The company reports more than 800 customers protected across the territories it serves.
DTS Solution
DTS Solution
+965 2244 7897
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
